Password Strength Myths? Busted
Password advice is full of folklore: change it every thirty days, never write it down, complexity beats length. Much of it is outdated or was never true — and following myths can leave you less safe than ignoring them. Here are the big ones, busted.
TL;DR / Quick Fix
Quick fix: length beats complexity, forced monthly changes backfire, and writing passwords in a manager beats memorizing weak ones. The myths persist because they sound strict. What actually works: long unique passwords, a manager, and two-factor on important accounts — not calendar reminders to rotate seasonal passwords.
Follow these steps
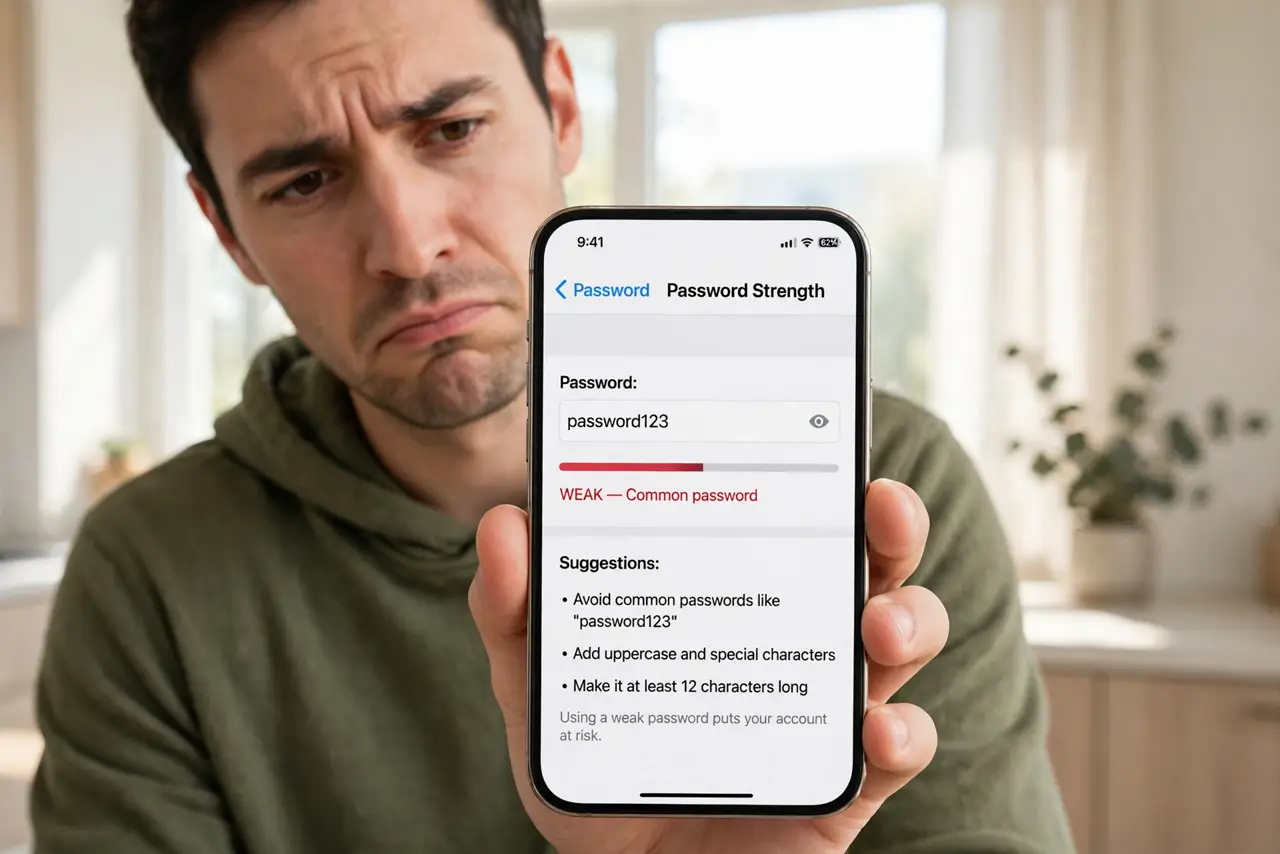
- Myth: complex beats long. Busted: short 'complex' passwords fall to guessing lists fast, while a four-word passphrase resists far longer. Length is the dominant factor — complexity is a distant second.
- Myth: change passwords monthly. Busted: forced rotation makes people pick weaker, predictable passwords ('...January,' '...February'). Change on suspicion of breach, not on schedule.
- Myth: never write passwords down. Busted: a password manager is 'writing them down' done right — encrypted, backed up, searchable. A sticky note is the problem, not the concept.
- Myth: security questions are a safe backup. Busted: your mother's maiden name is public record. Treat them as weak passwords, not safety nets — see why security questions fail.
- Myth: SMS codes mean you are fully protected. Half-busted: SMS two-factor beats nothing, but SIM-swap attacks can intercept codes. An authenticator app is the stronger second factor — compare app vs SMS.
- Myth: a strong password alone is enough. Busted: breaches leak even strong passwords. Unique-per-site plus two-factor is the real standard — strength is only one leg of it.
What NOT to do
- Do not rotate passwords on a calendar. Schedule-driven changes produce predictable patterns attackers love.
- Do not trust old 'complexity score' meters blindly. Many reward short complex passwords that sit on every guessing list.
- Do not believe hackers target other people. Automated attacks try everyone; obscurity is not protection.
- Do not treat myths as harmless. Each one costs effort better spent on what works: unique passwords and two-factor.
Frequently asked questions
Should I really not change my password regularly?
Correct — unless there is a breach or suspicion. Modern guidance says long, unique, and stable beats short, rotated, and predictable.
Is writing passwords in a notebook okay?
A notebook at home beats reuse, but a password manager beats the notebook: encrypted, backed up, and it autofills so you are not typing.
What is the single biggest password myth?
That complexity matters most. Length dominates the math — which is why passphrases win.